OpenID Connect
Follow these steps to configure Okta OIDC for your application:
1. Sign Up for an Okta Developer Account
- Navigate to the Okta Developer Signup page: developer.okta.com/signup/.
- Click on the Sign up for Integrator Free Plan.
- Fill out your details (First Name, Last Name, Work Email, Country/Region).
- Complete the reCAPTCHA and click on Sign up.
2. Verify Your Email Address
- After signing up, Okta will send a verification email to the address you provided.
- Check your inbox, open the email from Okta, and follow the link to verify your account to continue.
3. Set Up Security Methods
-
Once your email is verified, you will be directed to set up security methods for your account.
-
First, you need to set up a Password. Click on the Set up button under the Password section.
-
Next, you will be required to set up Okta Verify. Click on the Set up button under the Okta Verify section.
-
Download the Okta Verify app on your mobile device (iOS or Android).
-
Open the app, follow the instructions to add an account, and scan the QR code displayed on your screen.
-
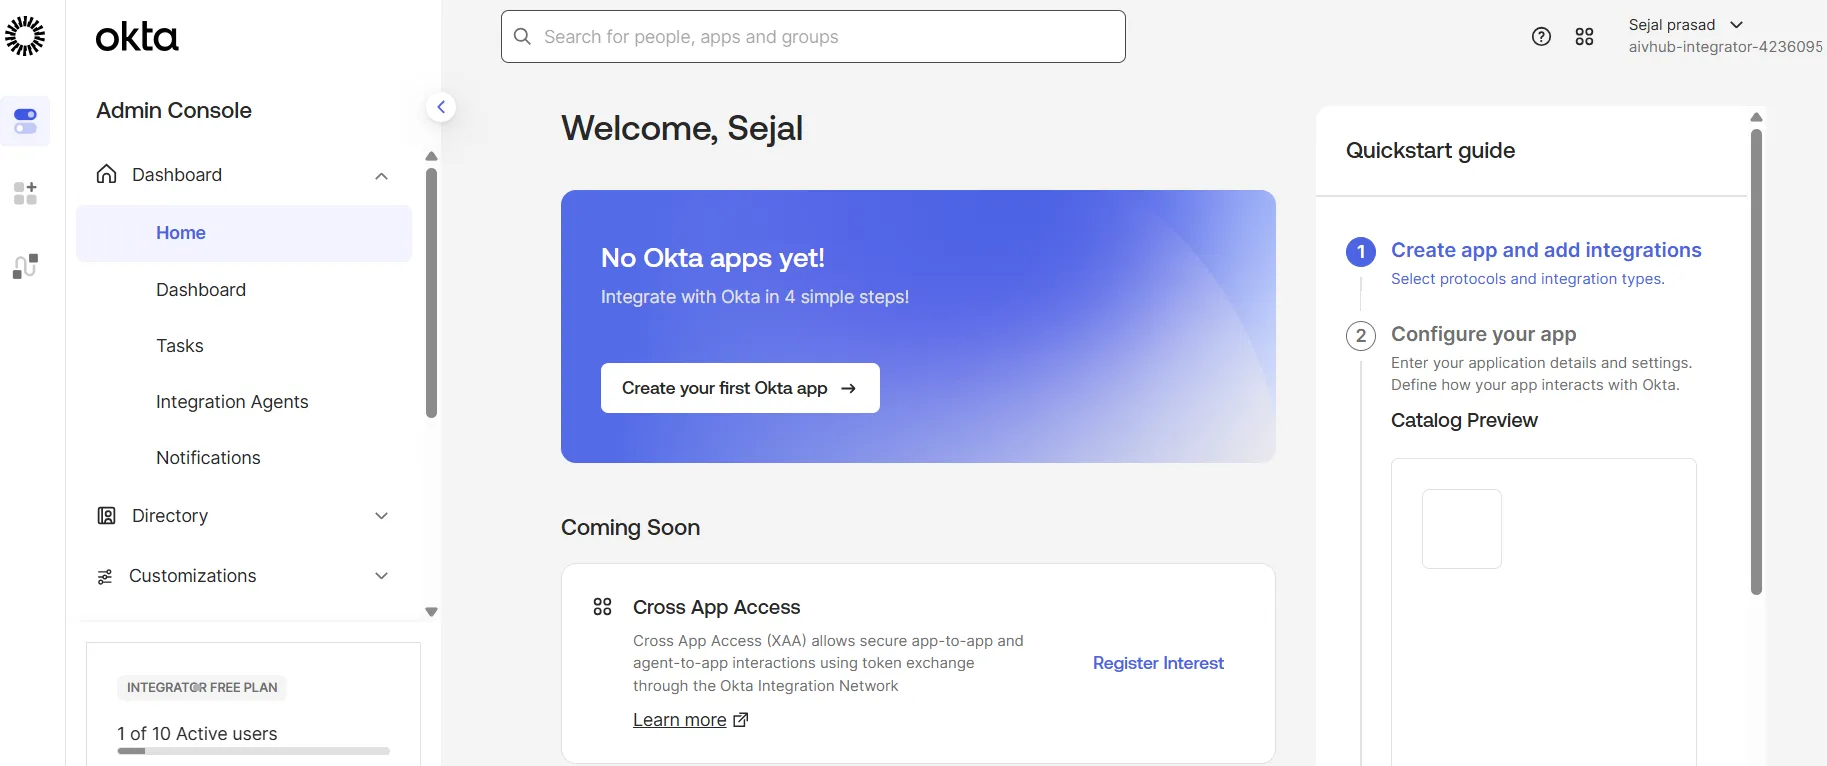
Once configured, it will take you to your Okta Admin Console, e.g., integrator-4236095.okta.com.
4. Create App Integration
-
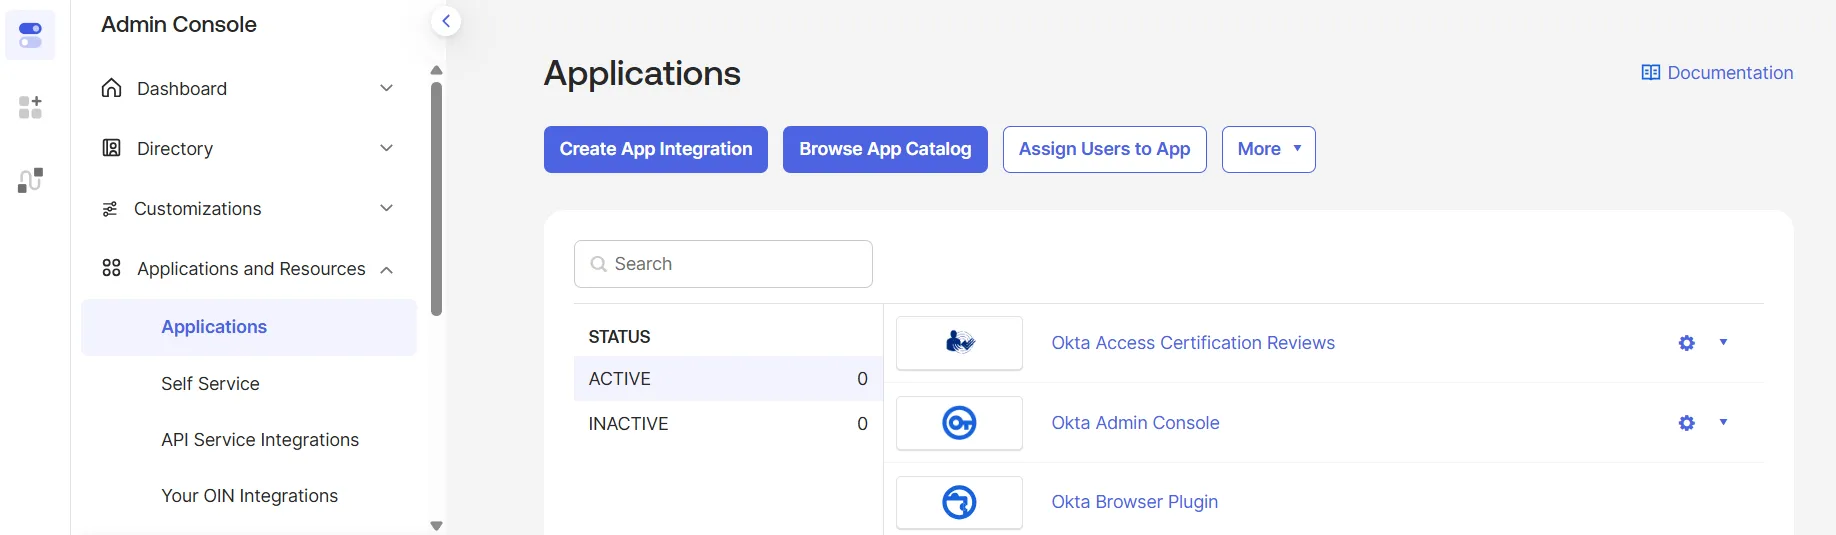
In the Okta Admin Console, navigate to Applications and Resources > Applications from the left sidebar.
-
Click on the Create App Integration button.
-
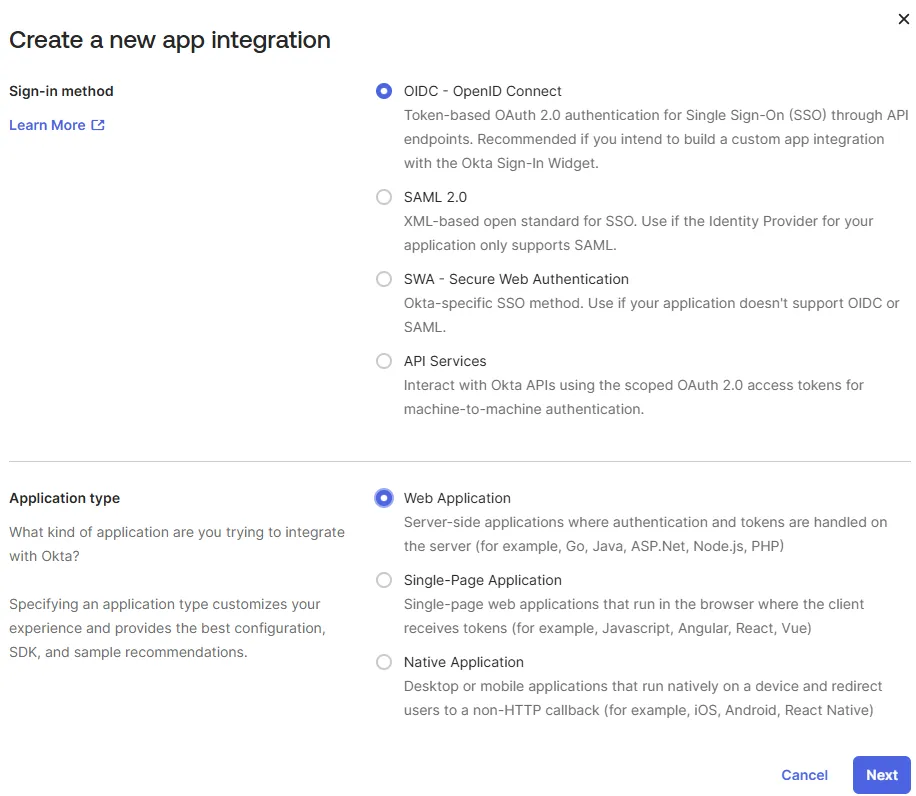
In the Create a new app integration dialog:
-
Select OIDC - OpenID Connect as the Sign-in method.
-
Select Web Application as the Application type.
-
Click Next.
-
-
In the New Web App Integration page under General Settings:
-
Enter an App integration name (e.g., “My Web App”).
-
Ensure Authorization Code is checked under Grant type.
-
In the Sign-in redirect URIs field, enter your application’s callback URL (e.g.,
https://<your_domain_name>/oauth/callback/oidc).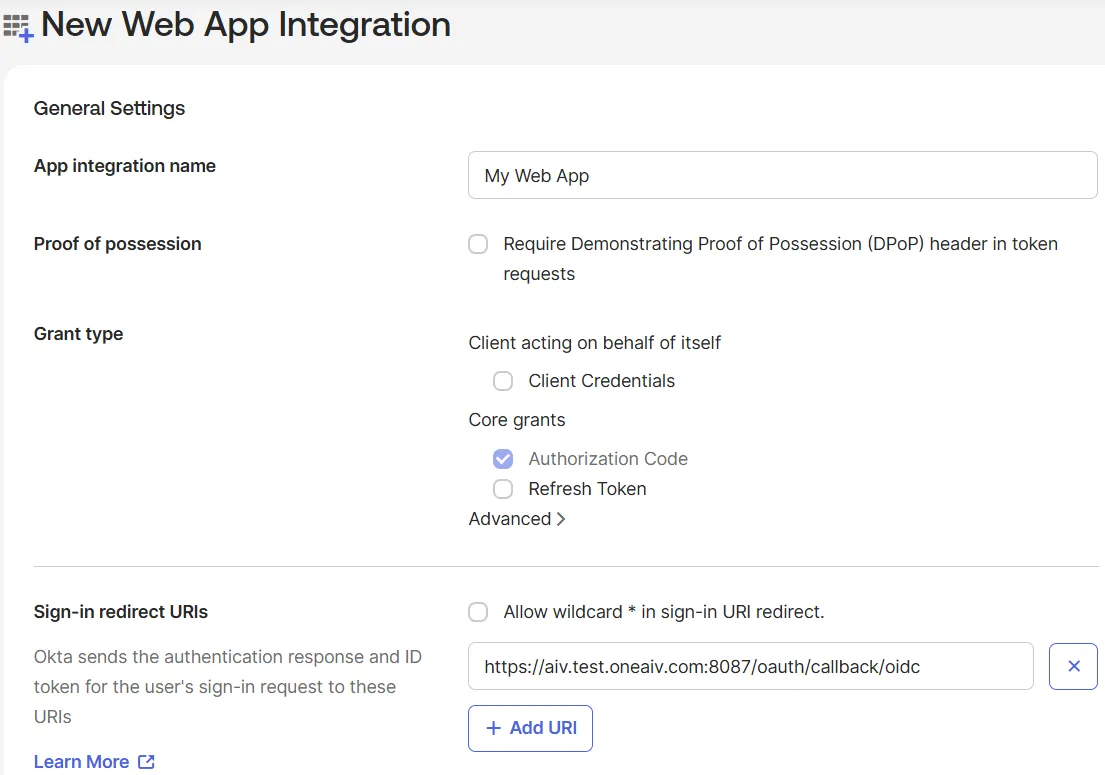
-
-
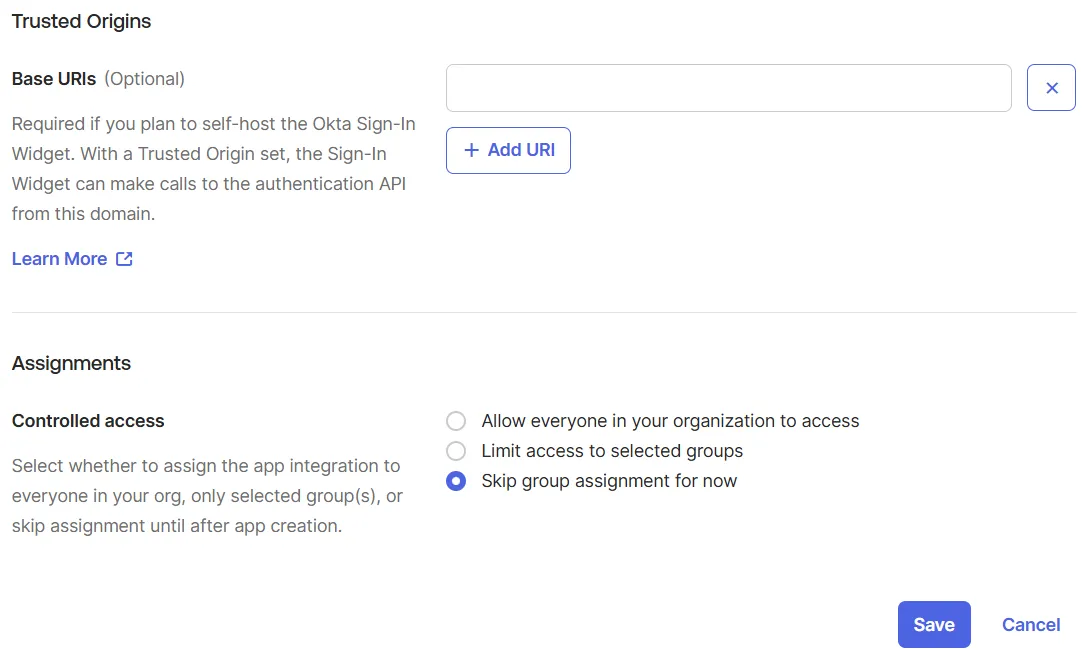
Scroll down to the Assignments section:
-
Under Controlled access, select Skip group assignment for now.
-
Click Save.
-
-
After the application is created, stay on the General tab.
-
Copy the Client ID and Client secret values. You will need to enter these into your AIV OIDC configuration.
-
Navigate to the Sign On tab.
-
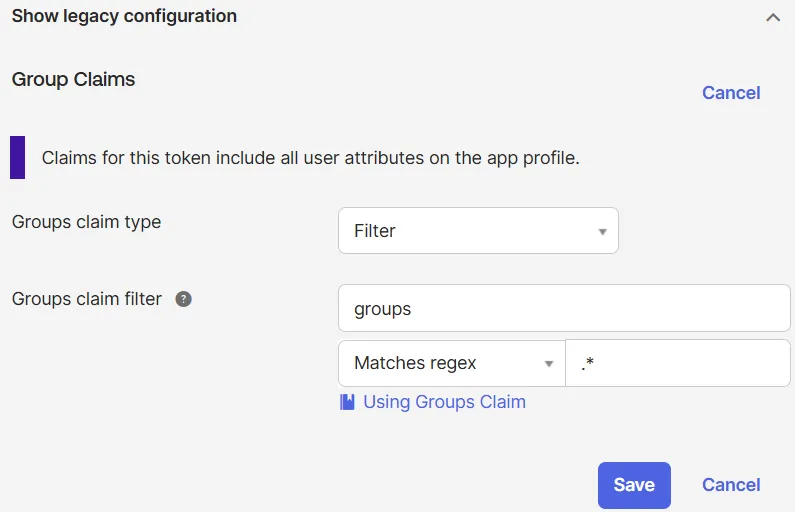
Scroll down to the Group Claims section (you may need to click Edit or expand Show legacy configuration) and configure the following:
-
Groups claim type: Select Filter.
-
Groups claim filter: Enter
groups, choose Matches regex, and enter.*. -
Click Save.
-
-
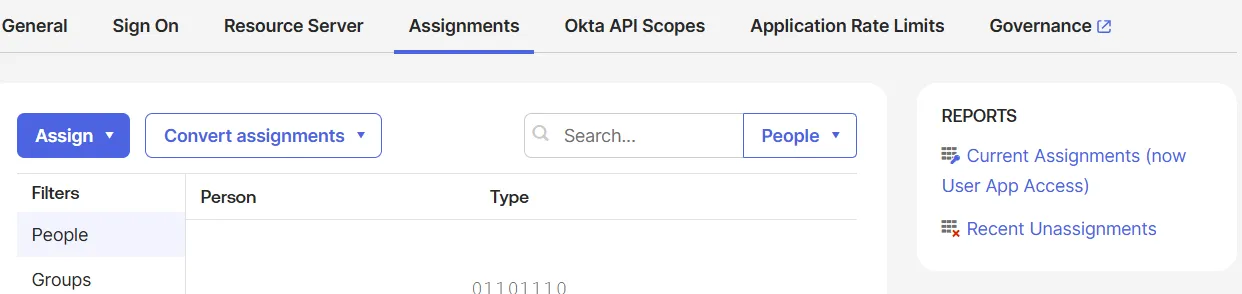
Next, navigate to the Assignments tab.
-
Click on the Assign dropdown and select Assign to People.
-
In the Assign My Web App to People dialog, click Assign next to the user(s) you want to grant access to.
-
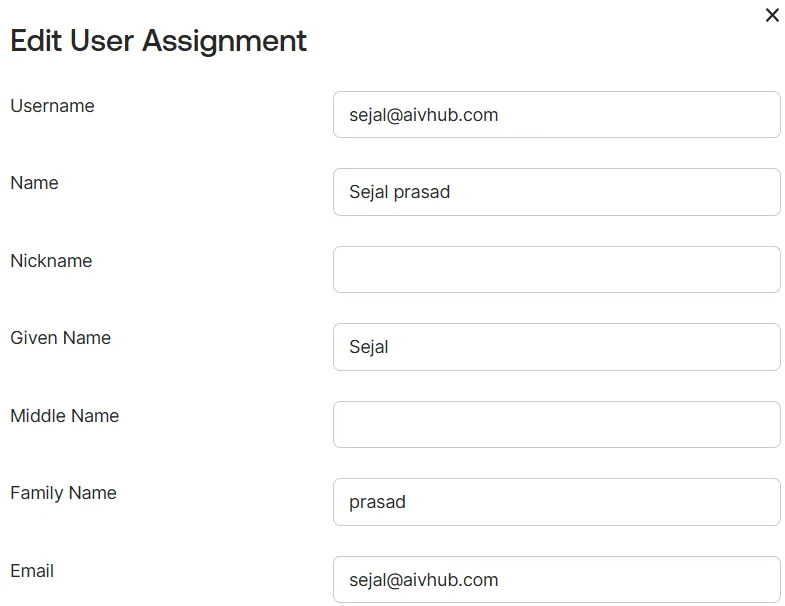
A profile attributes form will appear. Review the details and click Save and Go Back.
-
Click Done when finished.
-
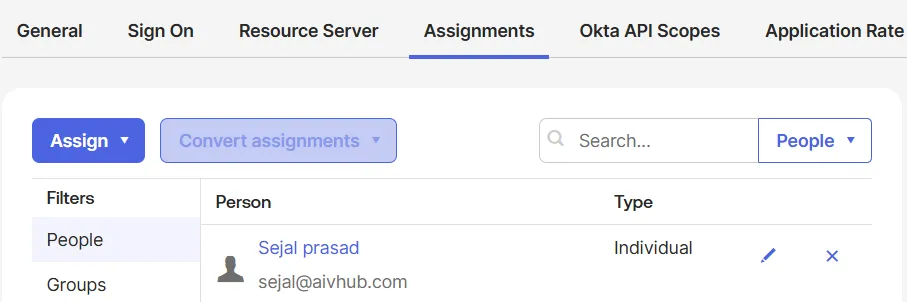
You will now see the assigned users listed under the Assignments tab.
5. Configure Authentication in AIV
-
Log in to your AIV application.
-
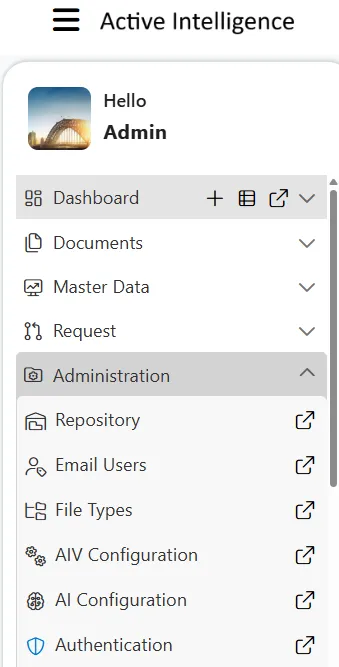
Click on the Hamburger menu (three horizontal lines) in the top-left corner to open the sidebar.
-
Expand the Administration section and click on Authentication.
-
The Universal Auth Administration page will open. From the left-hand directory menu, select Providers.
-
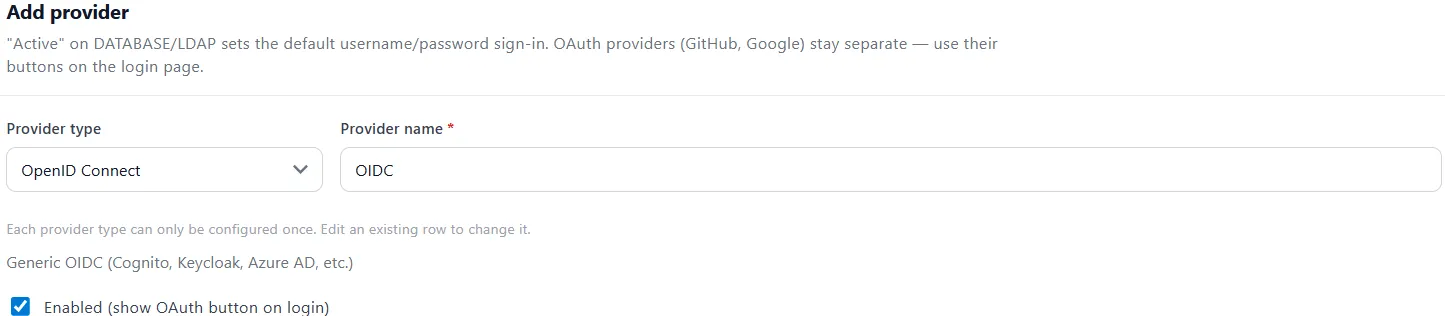
Under the Add provider section, locate the Provider type dropdown. By default, it will be set to Database (already configured).
-
Click the dropdown and select OpenID Connect.
-
Fill in the following details for the new provider:.
-
Provider name:
OIDC(or your preferred name) -
Priority:
100 -
Make sure to check the box for Enabled (show OAuth button on login).
-
-
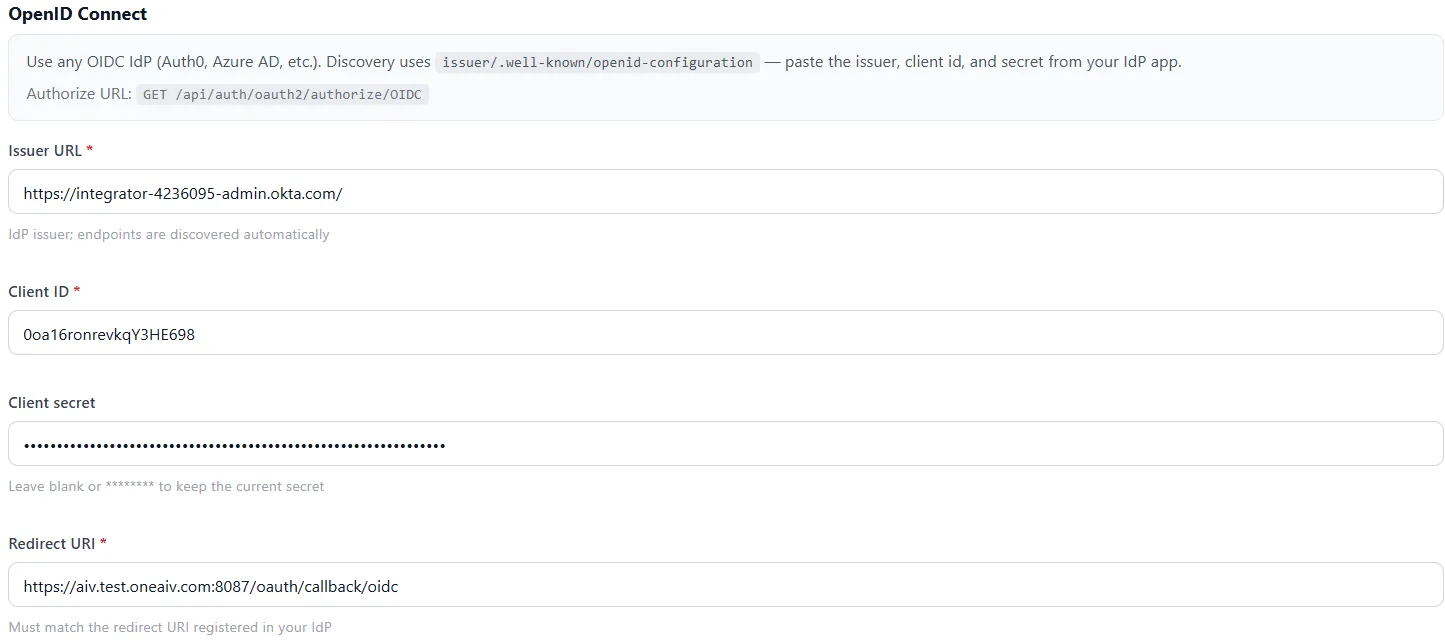
Scroll down to the OpenID Connect section and fill in the following details:
-
Issuer URL: Enter your Okta domain (e.g.,
https://integrator-4236095.okta.com/).- How to find it: You can find your Okta domain in the Okta Admin Console (e.g., if your admin URL is
https://integrator-4236095-admin.okta.com/, the issuer URL is typically the same).
- How to find it: You can find your Okta domain in the Okta Admin Console (e.g., if your admin URL is
-
Client ID: Enter the Client ID from Okta.
- How to find it: Go to your Okta Admin Console. Navigate to your application’s General tab and copy the Client ID.
-
Client secret: Paste the Client Secret generated from your Okta app.
- How to find it: On the same General tab in your Okta application settings, copy the Client secret.
-
Redirect URI: Enter the callback URL for your AIV instance (e.g.,
https://<your_domain_name>/oauth/callback/oidc).-
How to find it: This is the exact same URL you entered in the Okta Sign-in redirect URIs setting during the app creation step.
-
-
Scopes: Enter
openid profile email groups.
-
-
Click on the Add provider button to save.
-
A success popup message will appear, and you will now see your newly created Okta authentication provider listed as Active in the Provider configuration list.

6. Test the Okta Integration
-
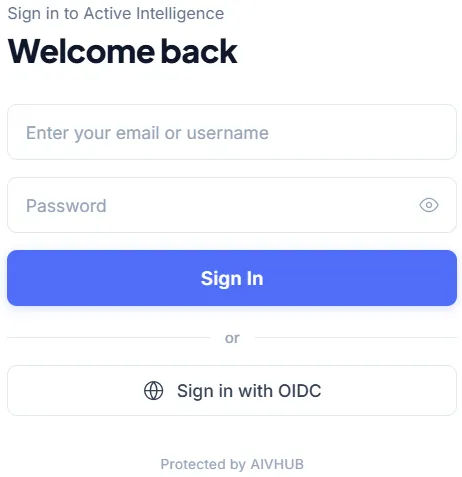
Log out of your AIV application (or open an incognito window) and navigate to your AIV login page.
-
Click the Sign in with OIDC (or the name you configured) button.
-
You will be redirected to the Okta sign-in page. Enter your Username (e.g.,
sejal@aivhub.com) and click Next. -
If prompted to verify your identity, select Password (or your preferred security method).
-
Enter your Okta password and click Verify.
-
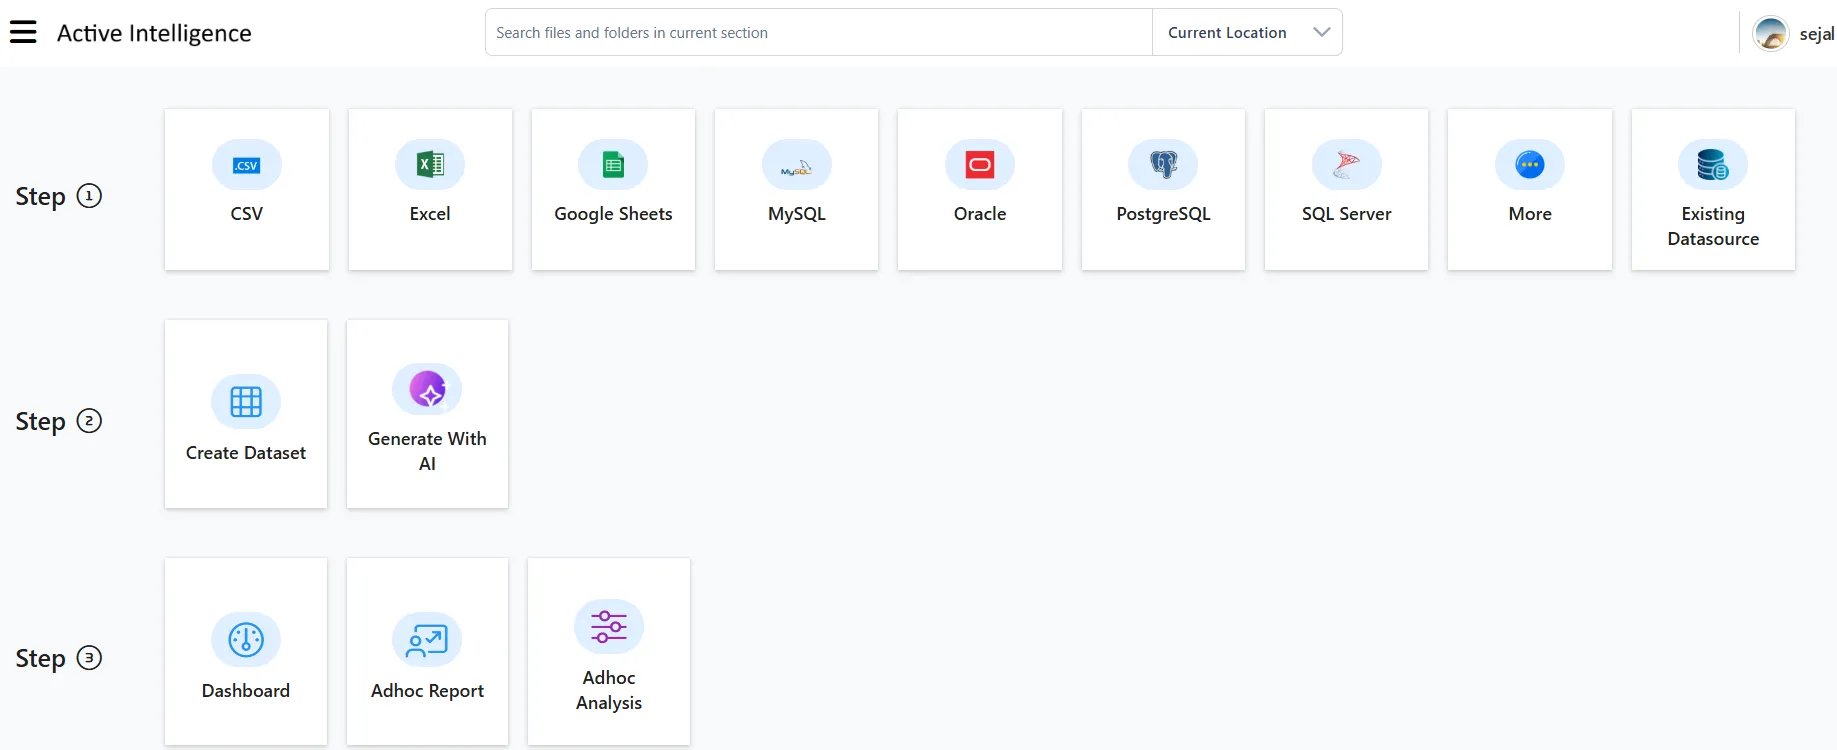
Upon successful authentication, you will be automatically redirected back to AIV and logged into your account.
Manage Role Synchronization
By default, users logging in via Okta OIDC are successfully authenticated but will not have any specific permissions within AIV.
Role synchronization allows you to map groups created in your Okta Directory directly to roles in AIV. When this is configured, AIV will read the user’s Okta group during login and automatically grant them the corresponding AIV role (and its associated permissions). This eliminates the need for an administrator to manually assign roles to new users inside AIV.
If you want to enable this automated role mapping, follow the steps below:
1. Create Groups in Okta
To begin, you must create groups in your Okta Directory that match the roles you plan to use in AIV.
-
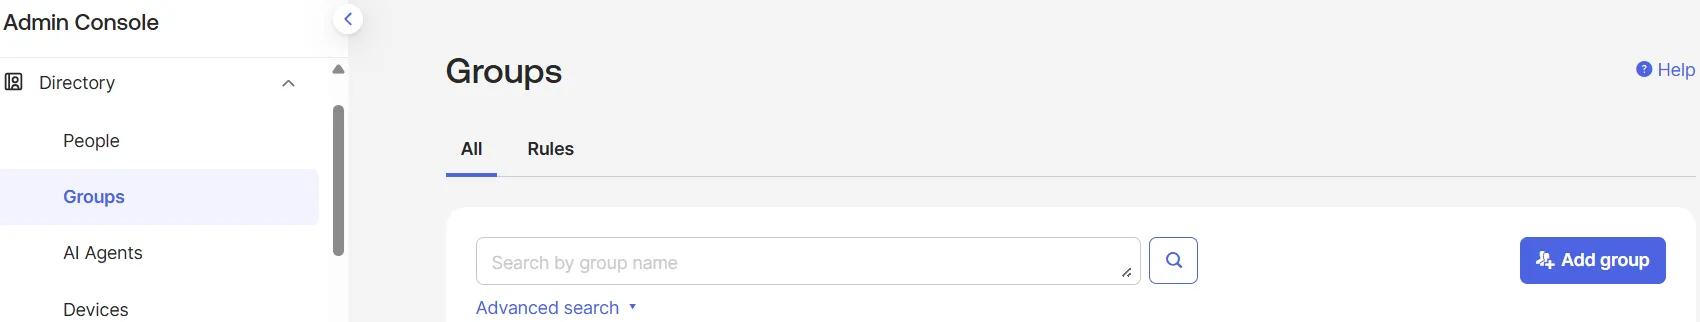
In the Okta Admin Console, navigate to Directory from the left-hand menu, expand it, and select Groups.
-
Click on the Add group button.
-
Add the necessary details for your group (e.g.,
HR Manager) and click Save.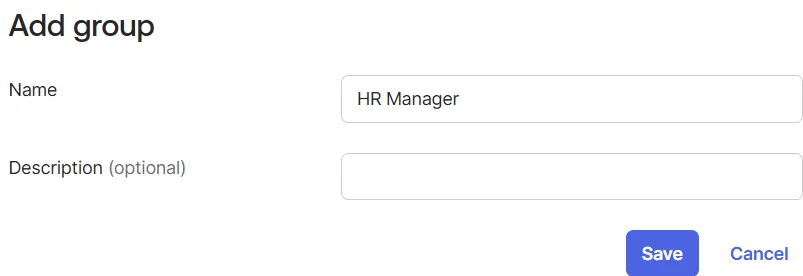
-
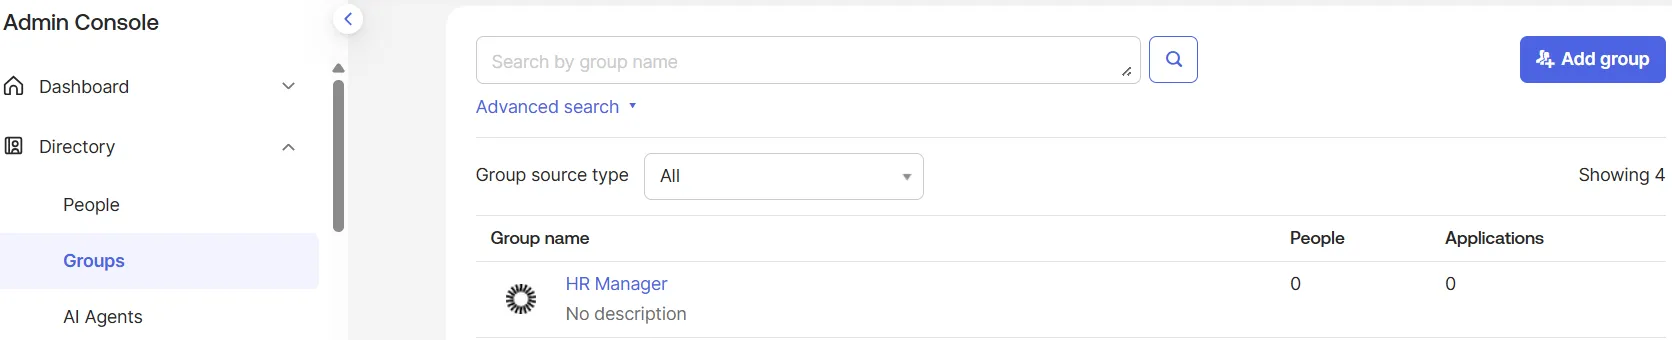
Once saved, your newly created group will show up in the Groups list.
-
Click on the group name (e.g., HR Manager).
-
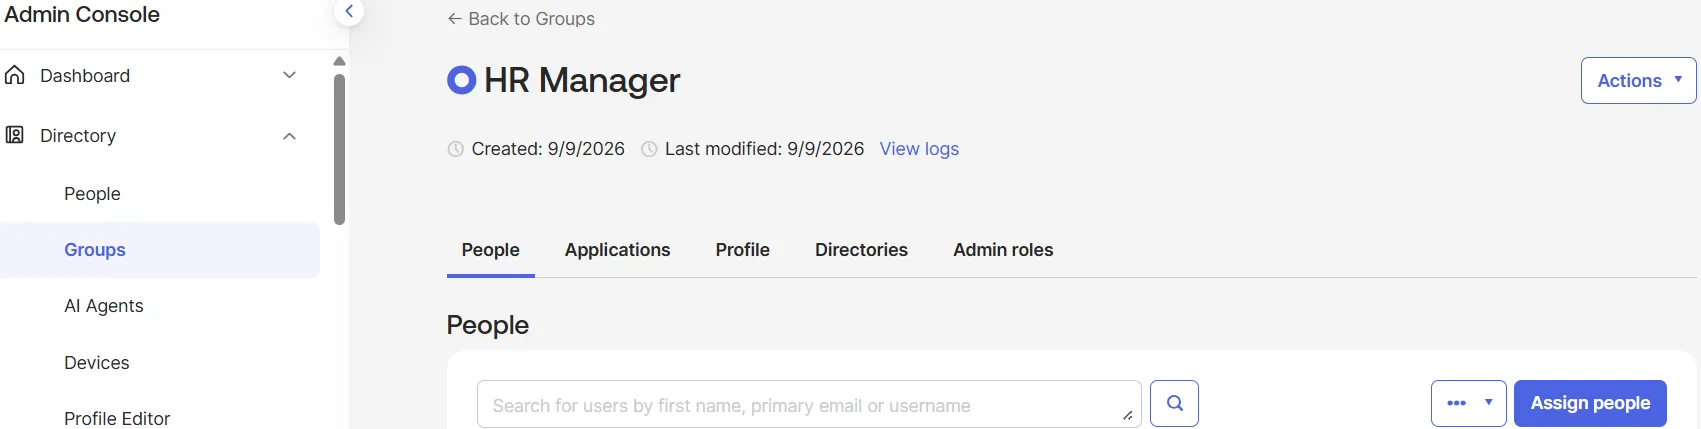
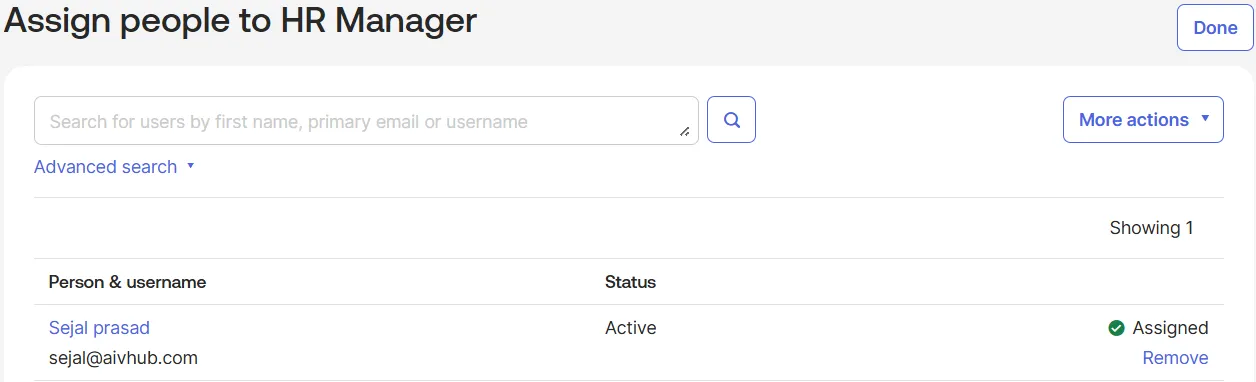
On the Group details page, go to the People tab.
-
Click on the Assign people button.
-
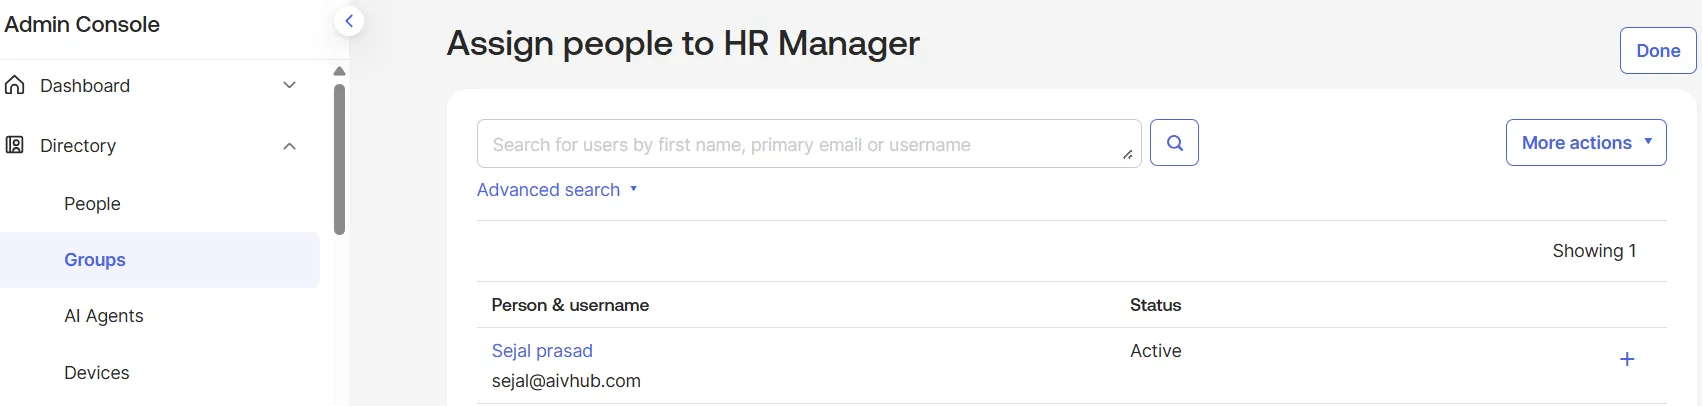
Click the + (or assign) button next to the users you want to assign to this group. Once the user shows as Assigned, click Done.
2. Create Role in AIV
Before verifying the role mapping, ensure that a role with the exact same name exists in AIV.
-
Ensure you are logged into your AIV application as a user with Universal Auth access.
-
Open the Hamburger menu (three horizontal lines) in the top-left corner.
-
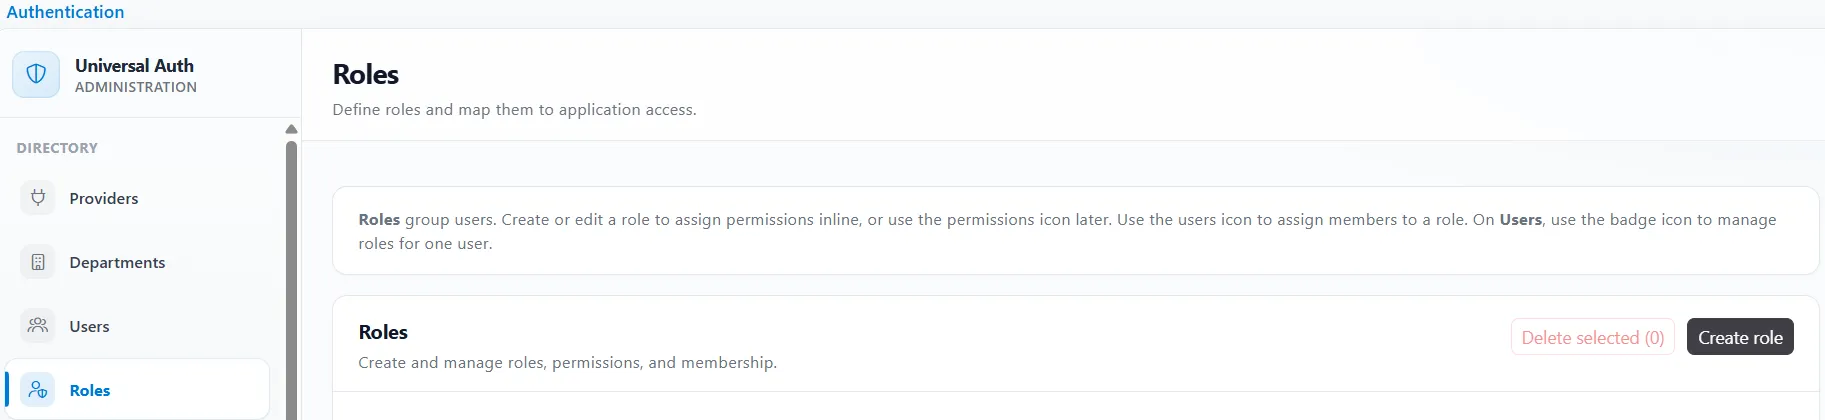
Expand the Administration section, click on Authentication, and then click on Roles.
-
Click on the Create role button.
-
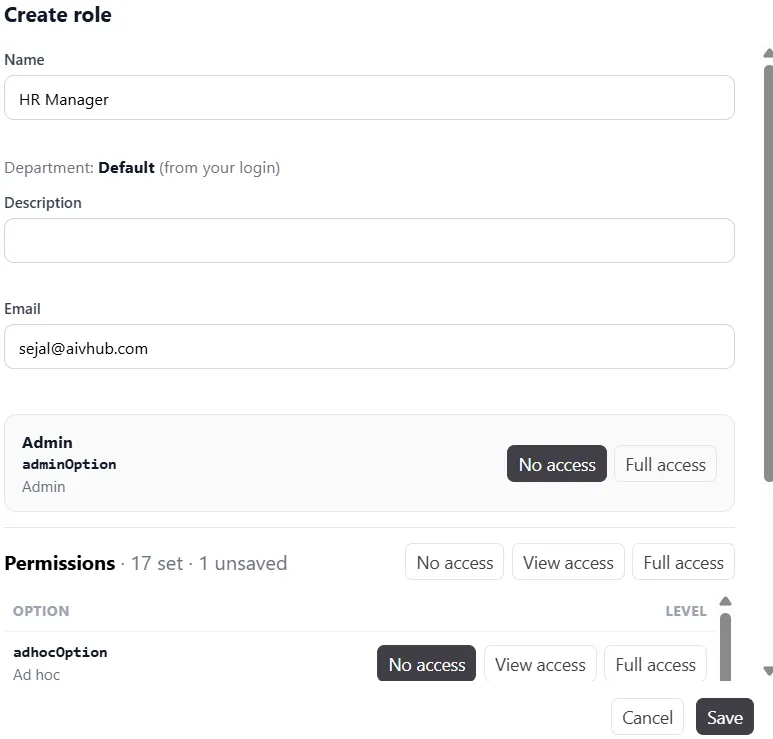
In the Name field, enter HR Manager to match the group created in Okta.
-
Provide any necessary permissions or descriptions, and click Save.
3. Enable Role Sync in AIV Provider Settings
-
Navigate back to Administration > Authentication > Providers in the AIV application.
-
Click on the Edit icon next to your active Okta OpenID Connect provider.
-
Scroll down to the Role sync on login section.
-
Check the box for Roles come from this provider.
-
In the Roles attribute / claim name field, enter
groups(or the specific claim your Okta configuration uses to pass group info).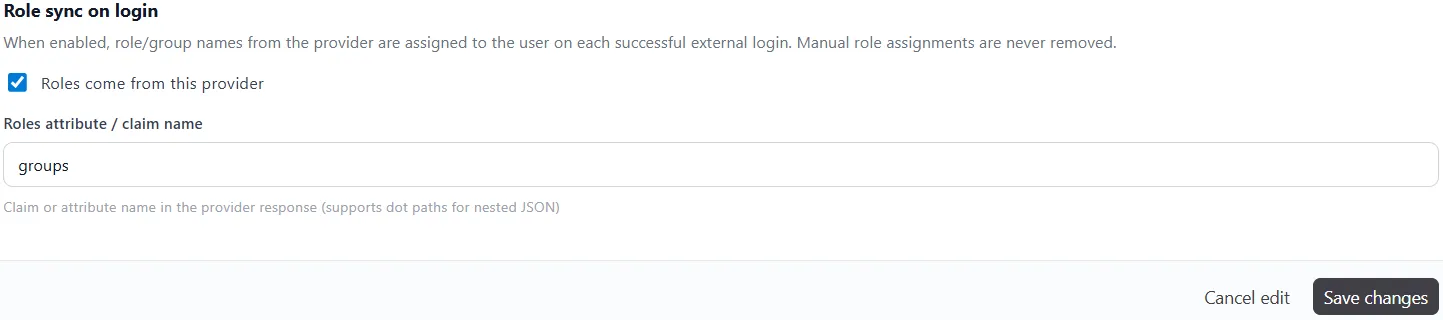
-
Click Save changes to finalize your setup.
4. Verify Role in AIV
-
Log out of your AIV application.
-
Log in again using the Okta OpenID Connect provider.
-
Upon logging in, the HR Manager role assigned in Okta will be automatically mapped to the user in AIV.
-
Open the Hamburger menu, expand the Administration section, click on Authentication, and then click on Roles.
-
In the Roles list, locate the HR Manager role and click on the Assign users icon next to it.
-
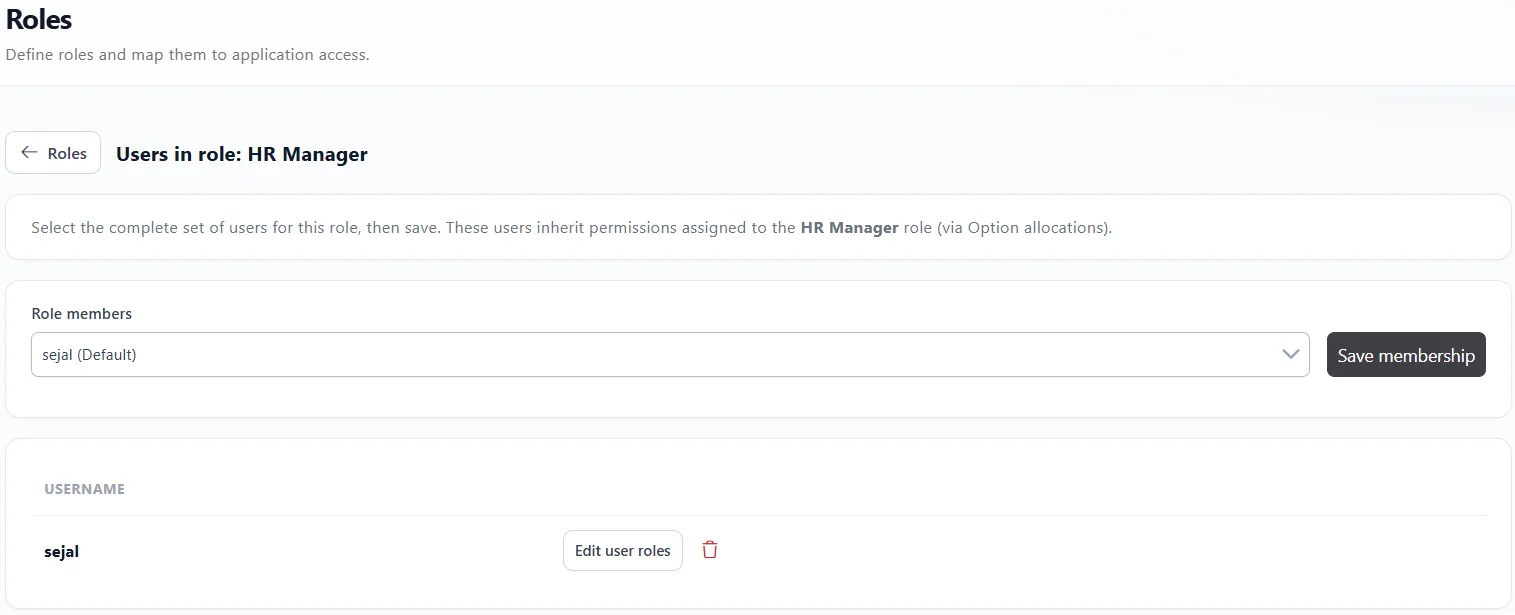
On the Users in role: HR Manager screen, you will be able to see that your logged-in user is successfully assigned to the HR Manager role.